Managed security operations center

Experts defending your organization around the clock. Our US-based SOC, built for critical infrastructure, monitors, detects and responds across endpoints, networks and cloud, with a dedicated analyst and threat hunter assigned to you.

SOC datasheetPDF, 2 pages

The SOC charts a week of threat activity, catches a spike on Wednesday and contains the threat by isolating a laptop.

What the SOC does.

A 24×7 distributed facility, working from your environment’s telemetry and the threats aimed at your sector.

01US-based SOC
Analysts based in the United States, supporting critical infrastructure, including water and wastewater systems, 24 hours a day, 7 days a week.
02Around-the-clock monitoring
Your endpoints, networks and cloud watched 24 hours a day, every day of the year.
03AI-enabled detection
Endpoint detection and response that correlates events with your topology, your industry’s threats and user behavior.
04Automated root cause analysis
Endpoint detections combined with environment telemetry to find where an incident started.
05Response across your controls
Incident response carried out through the security controls you already run, on premises and in the cloud.
06Cross-tool threat hunting
One view of your security posture across tools, so hunters find what single products miss.
07Vulnerability management
Vulnerabilities tracked and patch updates pushed, with reporting on what is left.

Every alert, on one timeline.

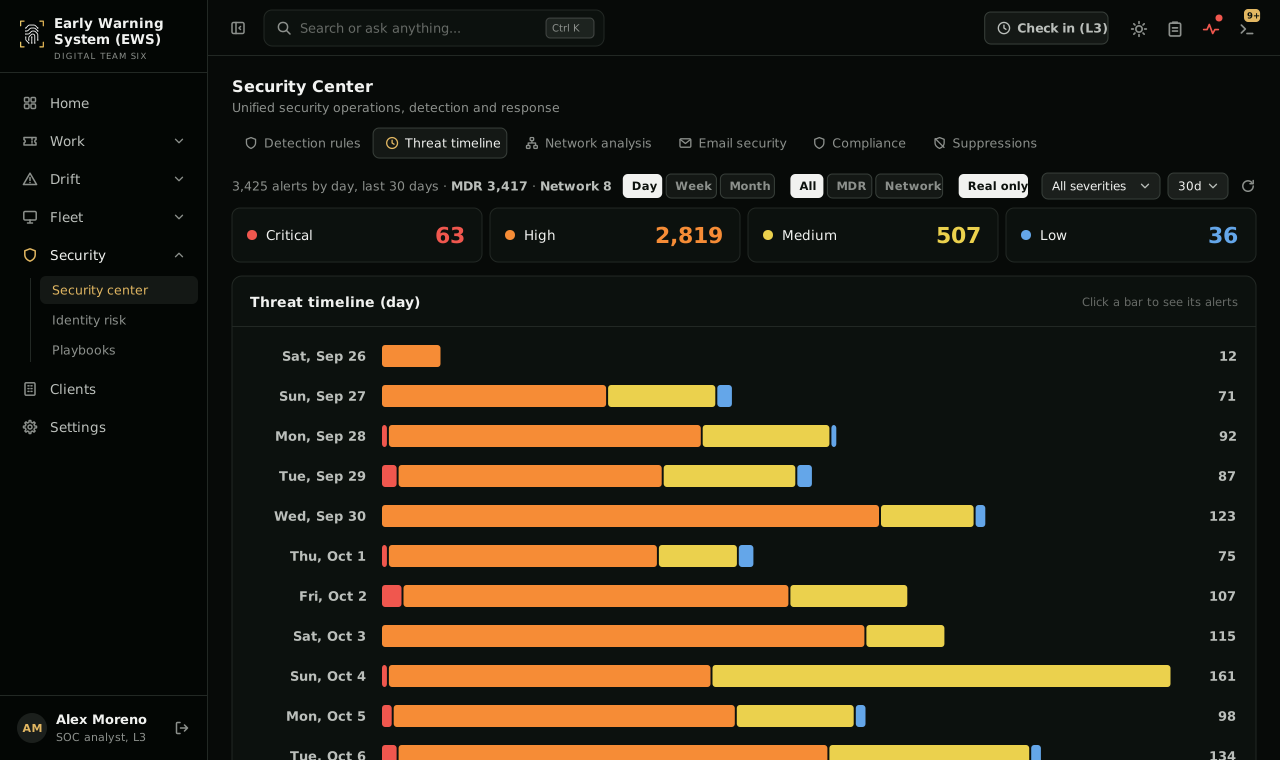
Detections from endpoints, network, email and cloud land in Culper-I, consolidated by day and graded by severity. Analysts open any day to work the alerts behind it.

Threat timeline

The Security Center threat timeline: 3,425 alerts over 30 days (63 critical, 2,819 high, 507 medium and 36 low), shown as one stacked bar per day from September 26, with daily totals between 12 and 161.
Security Center. Thirty days of alerts by severity, with managed detection and response and network sources broken out, and every day one click from its alerts.
Open full size: Threat timeline

Sample data. Clients, people, devices and addresses are illustrative.

A named analyst, not a ticket queue.

Every client gets a dedicated, US-based analyst and threat hunter who learns your environment, your people and your risks, and explains what they find in plain language.

  • A dedicated, US-based analyst and threat hunter
  • Automatic overview reports on your cyber health
  • Cyber risk analysis your leadership can act on
  • Training tailored to industry, regulatory and cyber insurance requirements

Keep the tools you have.

No rip and replace

The SOC integrates multiple vendors’ technologies, so you do not have to replace your existing security stack to get coverage.

Sees the plant too

Alerts from Culper-I go to analysts who understand control systems, so IT and OT incidents are handled together.

About Culper-I

Informed by your sector

Threat intelligence filters noise and adds context to every alert before an analyst sees it.

About threat intelligence

The result: incident reporting and insurance requirements met.

Monitoring, reporting and response around the clock, from a US-based team.

Incident reporting

24/7 detection and response, with what happened and what we did, ready for your report to NJCCIC or NYSDOH.

Wastewater systems

Network monitoring and logging, which New York requires of treatment works of 10 MGD or more.

Insurance

Monitoring, reporting and insurer-aligned training, the controls carriers ask about most.

Questions about the SOC.

In the United States. Our SOC is US-based and supports your operations 24 hours a day, 7 days a week, which many critical infrastructure operators now require.

Usually not. The SOC integrates with the controls you already own and recommends changes only where coverage is missing.

Your analyst confirms it, contains it through your integrated controls, and contacts you with what happened and what to do next.

Yes. Monitoring, reporting and insurer-aligned training are the controls carriers ask about most.

Put a security team on watch tonight.

Start with an assessment of what you run today, and where monitoring would close the biggest gaps.

Prefer to talk now? 973-339-0090