Zscaler discovered malicious campaign (Ruby Jumper) execution on air-gapped networks
At a glance
- Published
- February 27, 2026
- Written by
- Vijay Vedanabhatla
- Filed under
- Cybersecurity, ICS Security
- Reading time
- 1 minute
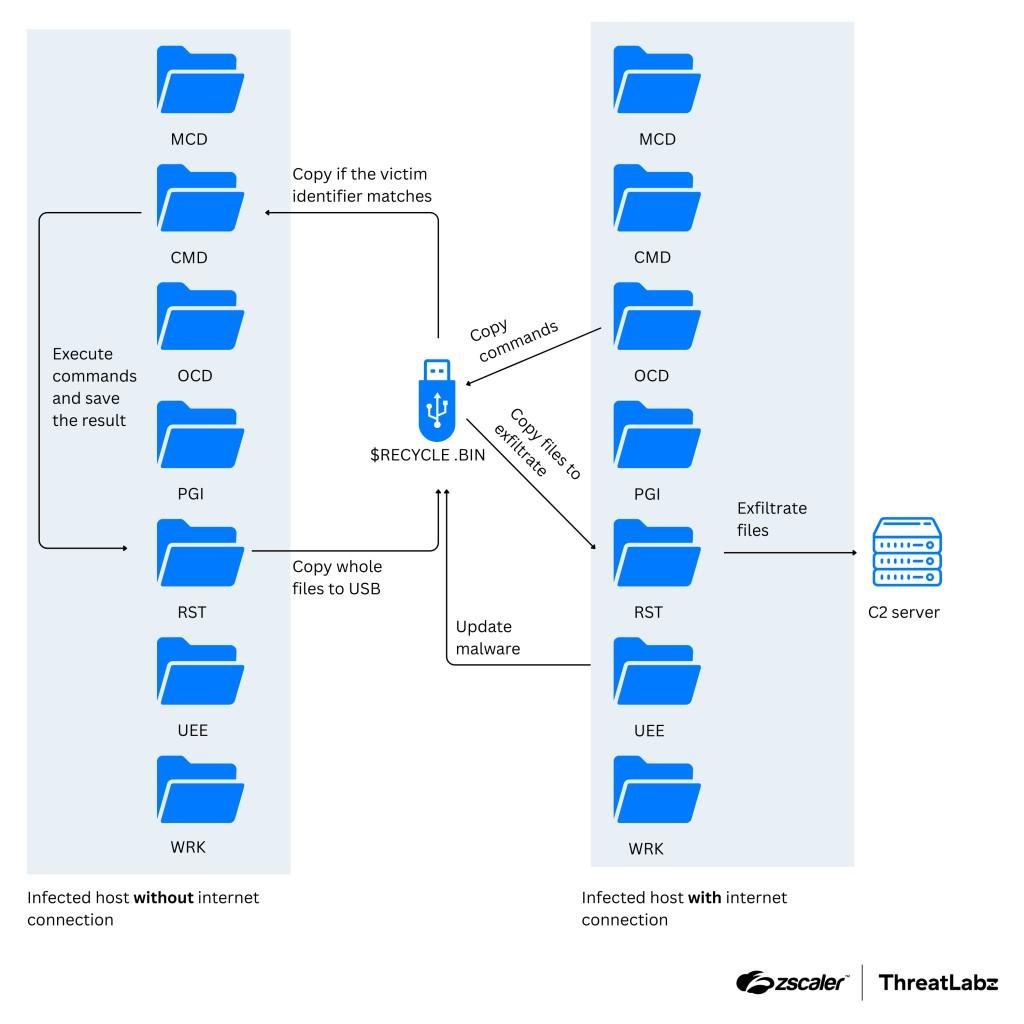
In December 2025, Zscaler ThreatLabz discovered North Korea state sponsored group APT37 employing malicious campaign called Ruby Jumper that’s capable of data exfiltration from air-gapped networks.
Detailed threat scenario from Zscaler research: APT37 Adds New Tools For Air-Gapped Networks | ThreatLabz
Use of malicious external hard drive / USB is nothing new, but this is a sophisticated threat scenario capable of creating a malicious bridge for air gapped network segments that’s typically used in critical infrastructure and industrial control systems implementations.
/01APT37 THUMBSBD attack flow for air-gapped systems
Keep reading.
September 2026
Culper-I Early Warning System (EWS) Subscription for WWS sector
Simultaneous cybersecurity attacks on water systems across twelve states from July 2026 have put Water and Wastewater Systems (WWS) critical infrastructure squarely in the…
Read the postAugust 2026
Why Water Utilities Remain a Soft Target for Cyber Threat Actors
In late July 2026, more than 25 water utilities across seven states reported cyber incidents linked primarily to internet-facing Programmable Logic Controllers (PLCs), weak…
Read the postApril 2026
ABCs to Modernize MUAs
Municipal Utility Authorities (MUAs) deliver essential services that communities depend on every day—clean drinking water, wastewater treatment, stormwater management, and in some cases local…
Read the postTalk it through with an engineer.
Tell us about your organization. One of our engineers will walk you through where you stand and where we would start.
Prefer to talk now? 973-339-0090